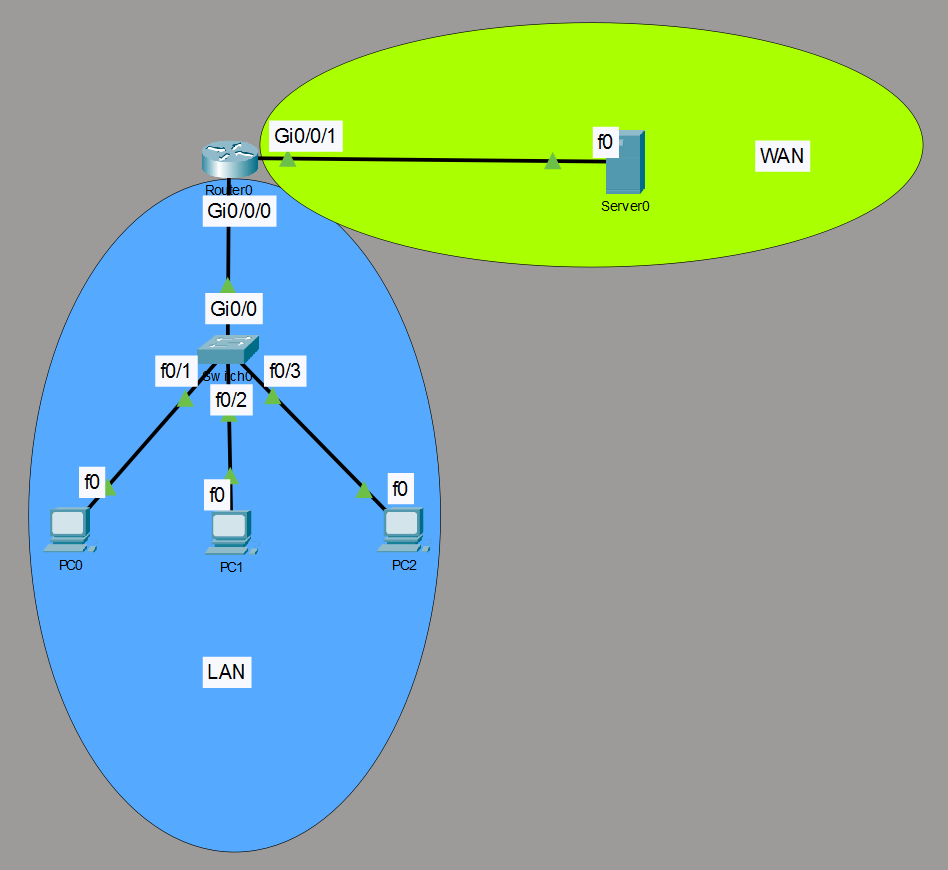
CCNA Lab 9: Hardening Remote Access with SSH
Unencrypted administrative access poses a major security risk in enterprise environments. Legacy protocols like Telnet transmit credentials and CLI sessions in cleartext, exposing management traffic to packet sniffing and man-in-the-middle attacks. Hardening remote access can be achieved by disabling Telnet, forcing SSH v2 for all Virtual Terminal (VTY) lines, and enforcing remote and/or local database authentication. Lab Objective: Disable insecure Telnet access on Cisco ISR router and Catalyst switch, configure RSA key pairs with SSH Version 2, build a local privilege 15 administrator account, and verify that unauthorized Telnet sessions are rejected. ...