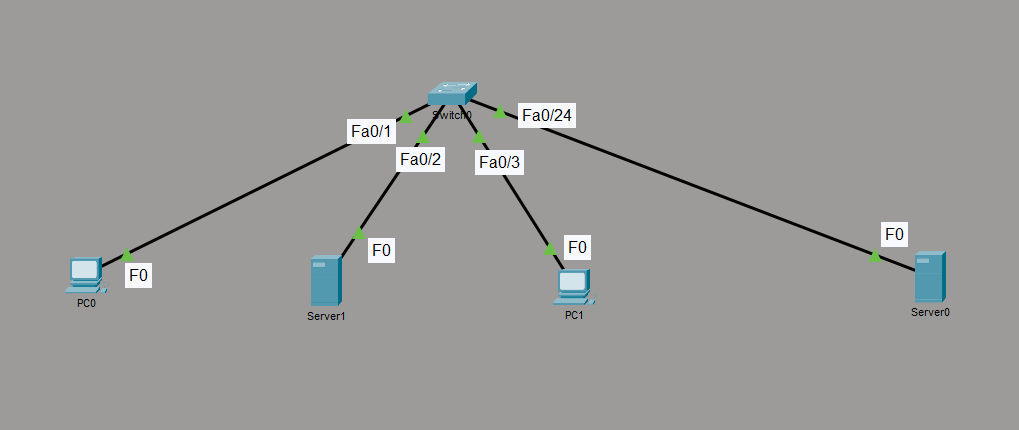
CCNA Lab 3: Layer 2 Security Hardening - DHCP Snooping, DAI, and Port Security
Lab Objective: Prevent rogue endpoints from acting as DHCP servers or spoofing ARP responses, and enforce dynamic MAC address binding to automatically shut down ports when unauthorized cable moves occur. 📁 Lab File: Download the Layer 2 Security Hardening Packet Tracer Lab (.pkt). Topology The topology uses a single Catalyst 2960 switch connecting legitimate endpoints, an authorized DHCP server, and a rogue device acting as a fake DHCP server. Source Device Interface Destination Device Interface Port Security Role PC0 (Legitimate Host) Fa0 Switch0 Fa0/1 Untrusted (Sticky MAC) Server1 (Rogue DHCP/Host) Fa0 Switch0 Fa0/2 Untrusted (Sticky MAC) PC1 (Legitimate Host) Fa0 Switch0 Fa0/3 Untrusted (Sticky MAC) Server0 (Legitimate DHCP) Fa0 Switch0 Fa0/24 Trusted (Infrastructure) Global Configuration (Switch) Enable DHCP Snooping and DAI globally, then mark the DHCP server port (Fa0/24) as trusted. ...